Analyzing Transaction Security Protocols in Austria's Licensed Online Gaming Sector
Yves Werner · Aug 21, 2026
Analyzing Transaction Security Protocols in Austria's Licensed Online Gaming Sector
Transaction security protocols form the backbone of Austria's licensed online gaming operations, where operators must meet strict technical standards set by national regulators to protect player funds and data during every deposit, withdrawal, and transfer. These measures align with broader EU financial regulations while addressing the specific risks that arise in real-time gaming environments, and they continue to evolve as technology and threat landscapes shift.
Regulatory Requirements for Payment Handling
Austria's Glücksspielgesetz and related ordinances require licensed operators to implement end-to-end encryption, segregated player accounts, and independent auditing of all financial transactions, with the Austrian Federal Ministry of Finance overseeing compliance through regular technical reviews. Operators must demonstrate that payment gateways meet PCI-DSS Level 1 standards before receiving or renewing licenses, and they must maintain these controls continuously rather than treating them as one-time checkboxes. Research from the PCI Security Standards Council shows that organizations maintaining continuous compliance experience fewer data breaches than those relying on annual audits alone.
Payment service providers working with Austrian licensees face additional scrutiny, including mandatory separation of gaming wallets from operational accounts and automated monitoring systems that flag unusual transaction patterns within seconds. These rules create a layered defense that combines regulatory oversight with operational technology.
Encryption and Data Transmission Standards
Licensed platforms rely on TLS 1.3 for all customer-facing connections, while internal systems handling settlement data often employ AES-256 encryption with rotating keys managed through hardware security modules. Data in transit between gaming servers and banking partners receives the same protection, and operators must document key rotation schedules during regulatory inspections. Observers note that these protocols reduce the window during which intercepted traffic could be decrypted even if keys are later compromised.
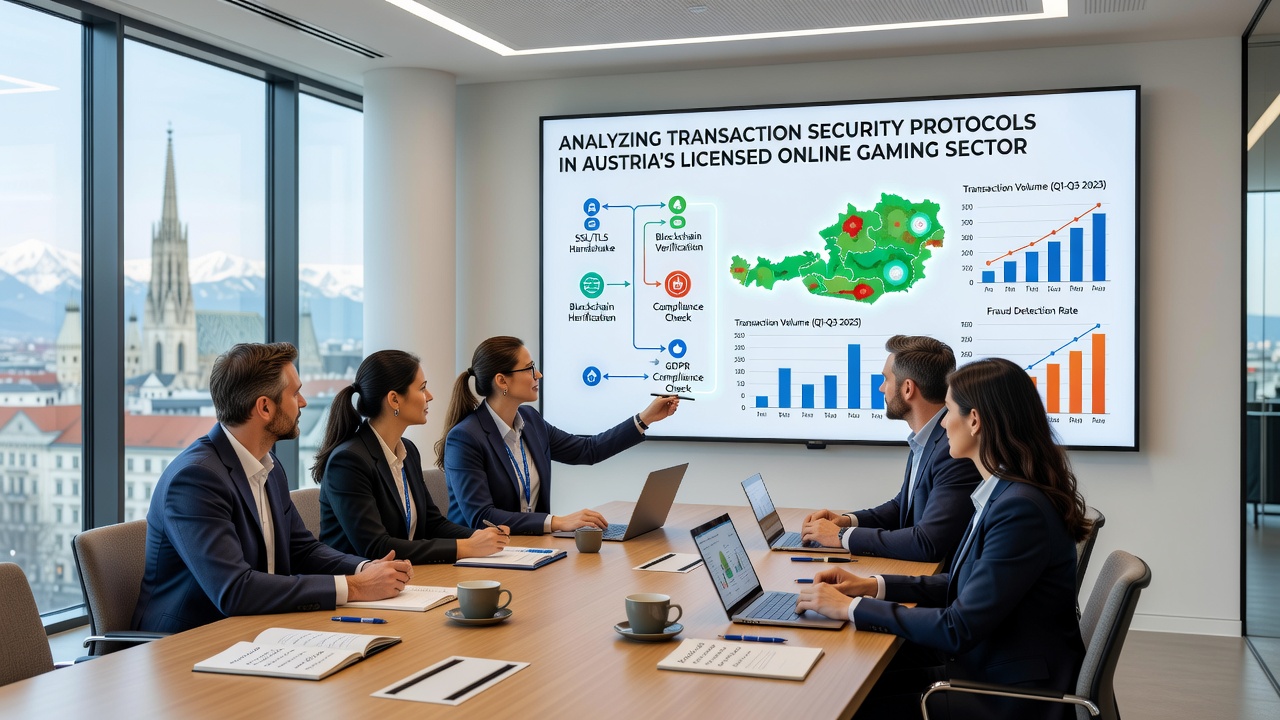
Multi-factor authentication now extends beyond login credentials to cover high-value withdrawals and account changes, with many platforms combining time-based one-time passwords and biometric verification on mobile apps. Transaction logs capture every authentication event and store them in immutable formats for at least five years, allowing forensic teams to reconstruct sequences during investigations. The second image illustrates a typical multi-layered authentication flow used across the sector.
Monitoring, Fraud Detection, and Incident Response
Real-time fraud detection engines analyze velocity, geolocation, device fingerprinting, and behavioral biometrics to identify potential account takeovers or money laundering attempts before funds leave the platform. When anomalies trigger alerts, systems automatically pause transactions and route them for manual review by compliance teams trained under Austrian gaming authority guidelines. European Commission reports on digital finance security indicate that such automated systems cut successful fraud rates by more than half in regulated markets that adopted them early.
Operators must also maintain documented incident response plans that include notification timelines to both regulators and affected players, with testing required at least annually. These plans cover scenarios ranging from payment processor outages to sophisticated social engineering attacks targeting customer support staff.
Developments Expected by August 2026
By August 2026, Austrian regulators plan to require enhanced API security standards for all third-party payment integrations, including mandatory mutual TLS authentication and stricter rate limiting. Licensed operators have begun pilot programs that incorporate these measures while maintaining backward compatibility with existing player interfaces. Industry associations report that early adopters see improved settlement times and reduced chargeback volumes once the new protocols stabilize.
Quantum-resistant cryptographic algorithms remain under evaluation rather than mandatory deployment, yet several larger licensees have already begun testing hybrid encryption schemes in controlled environments. These preparations reflect forward-looking risk management rather than immediate regulatory pressure.
Conclusion
Transaction security in Austria's licensed online gaming sector rests on a combination of prescriptive regulation, technical standards, and continuous monitoring that together create multiple independent layers of protection. As payment technologies advance and new threat vectors emerge, the framework continues to adapt through scheduled updates and collaborative testing between operators and regulators. The result is a system where security measures support rather than hinder player experience while meeting the stringent requirements of a fully licensed market.